 AsrielNetworks
What it does
- Ingests
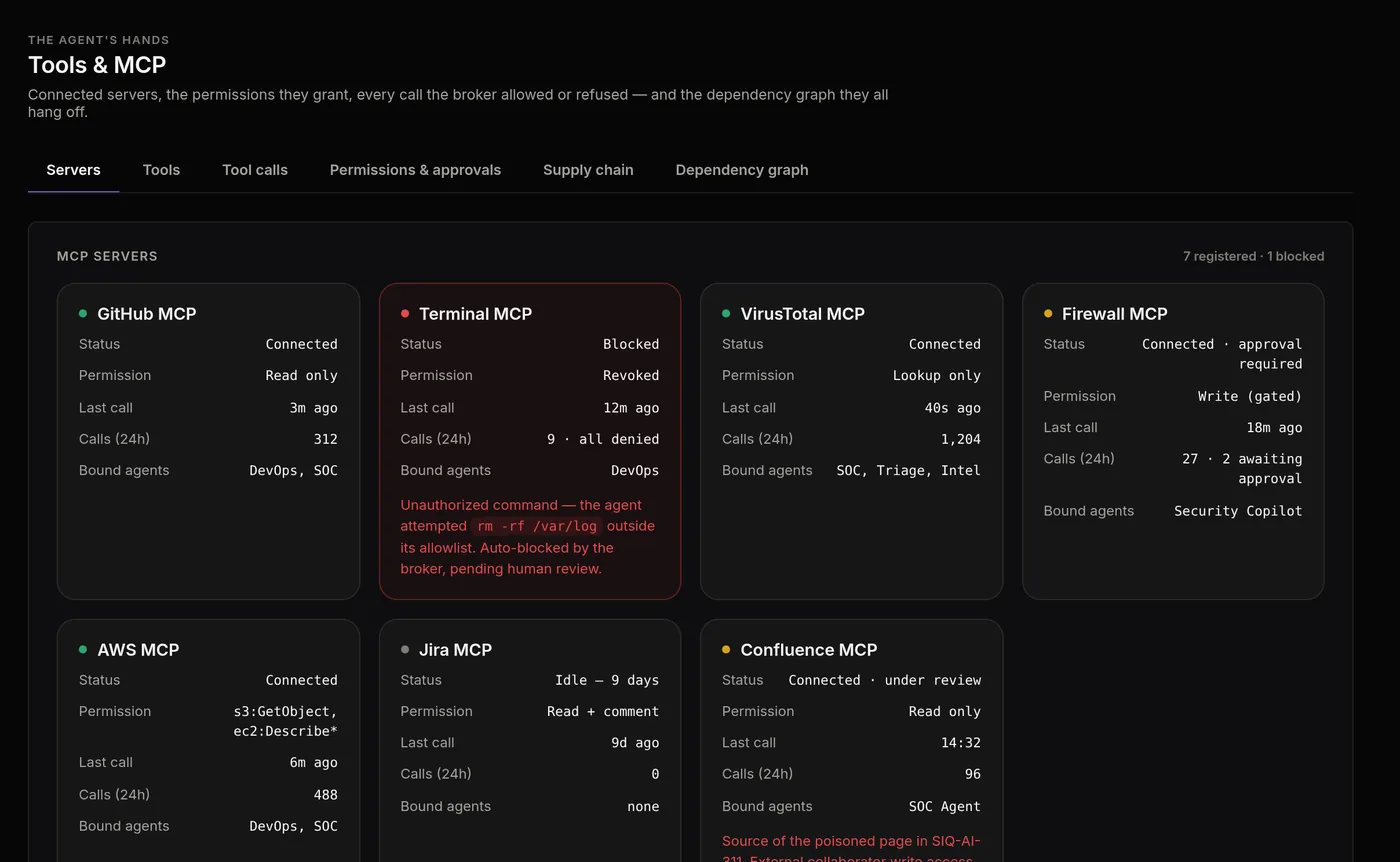
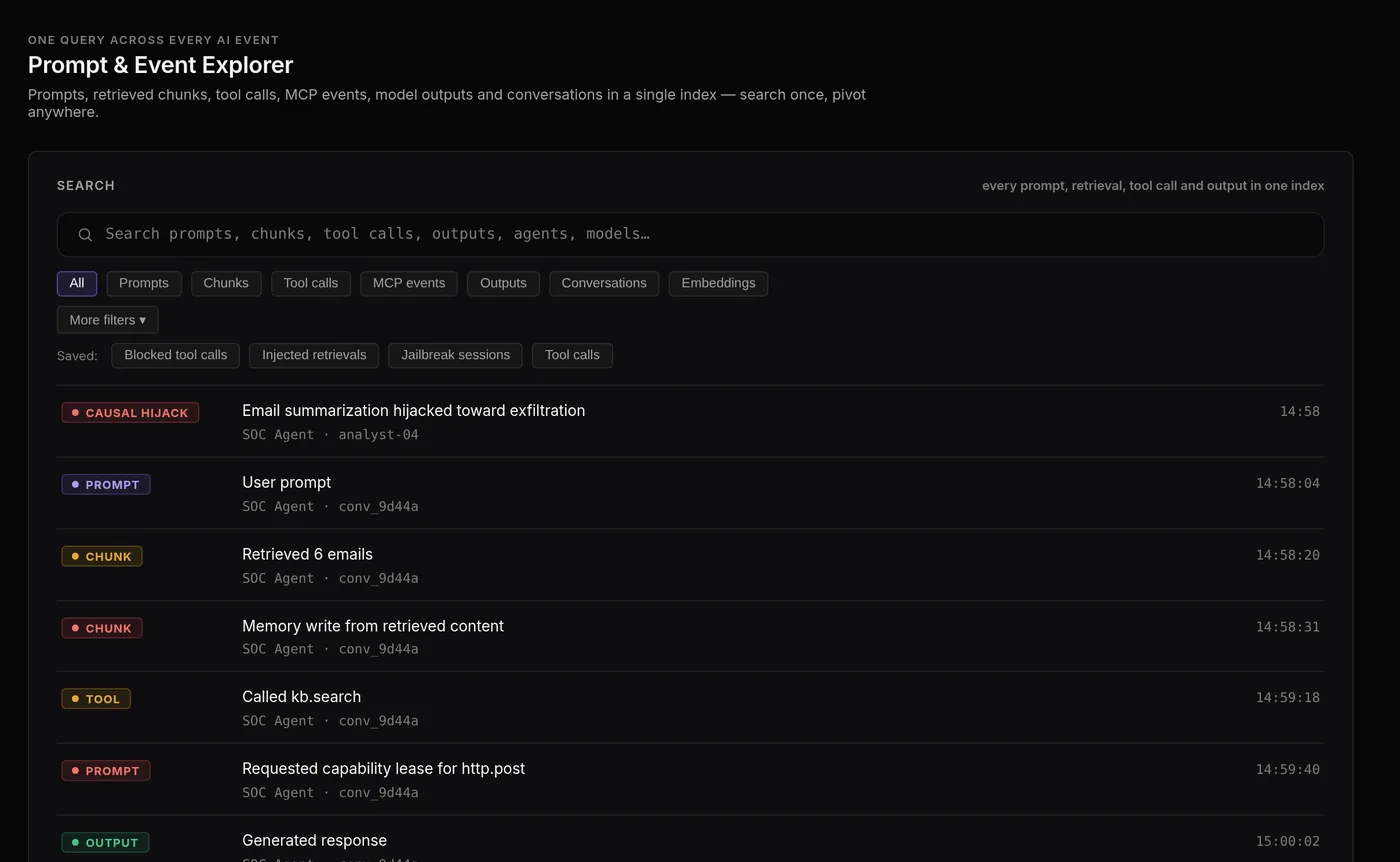
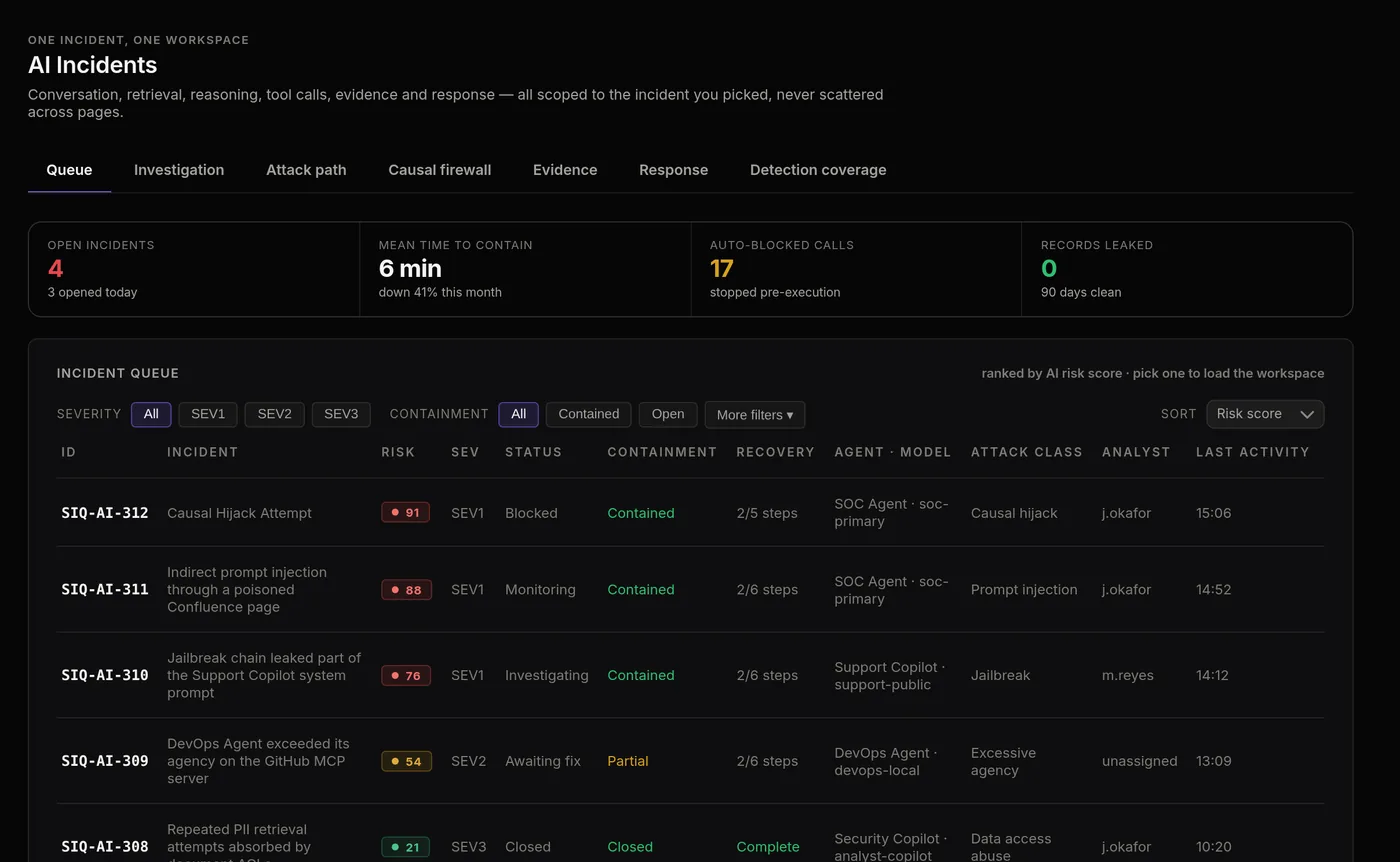
asrielnetworks.ai.event.v1telemetry from the SDK, a runtime path, or the inline gateway. - Runs the twelve built-in rules over each trace: prompt injection, excessive agency, data access abuse, supply chain, causal hijack.
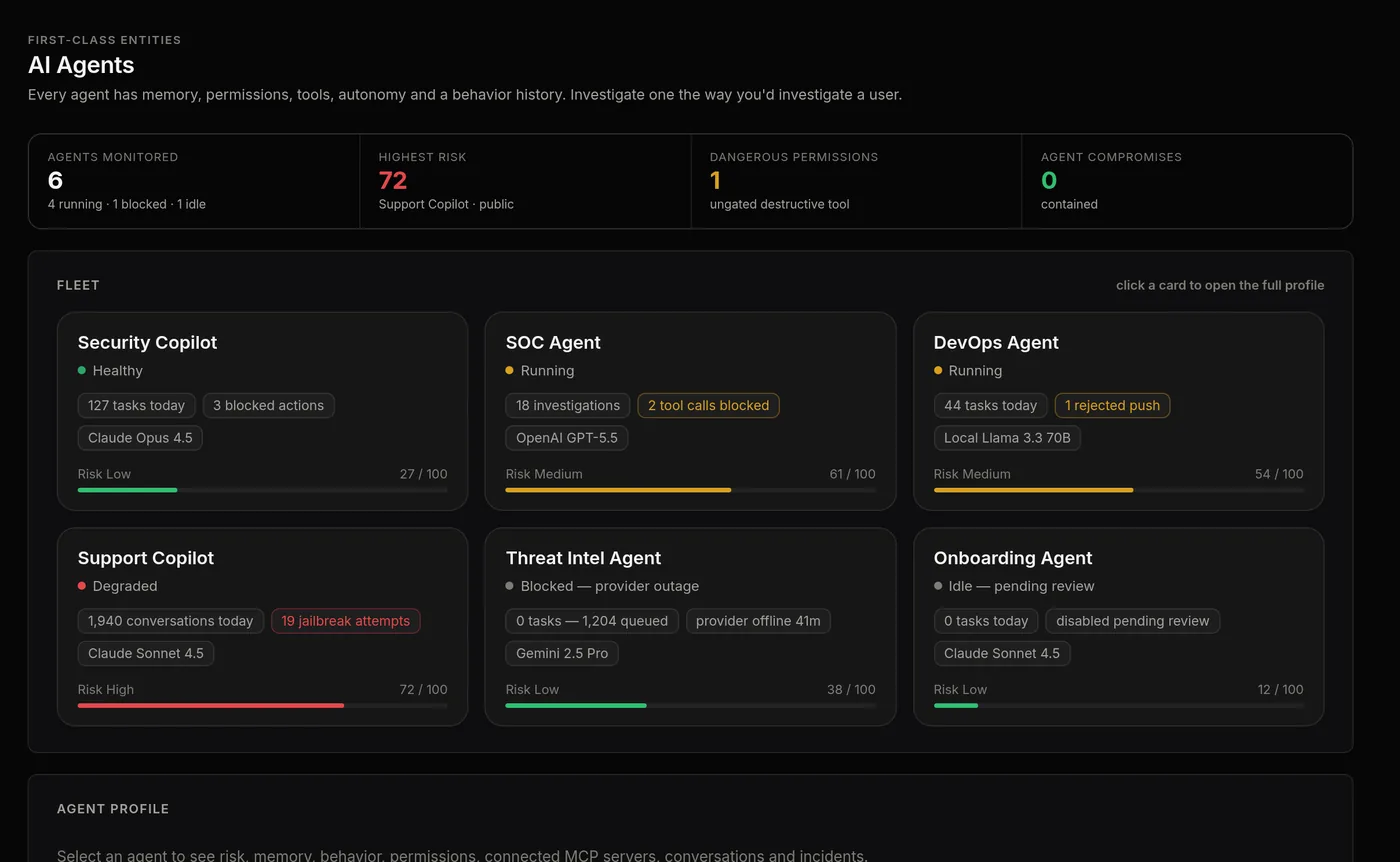
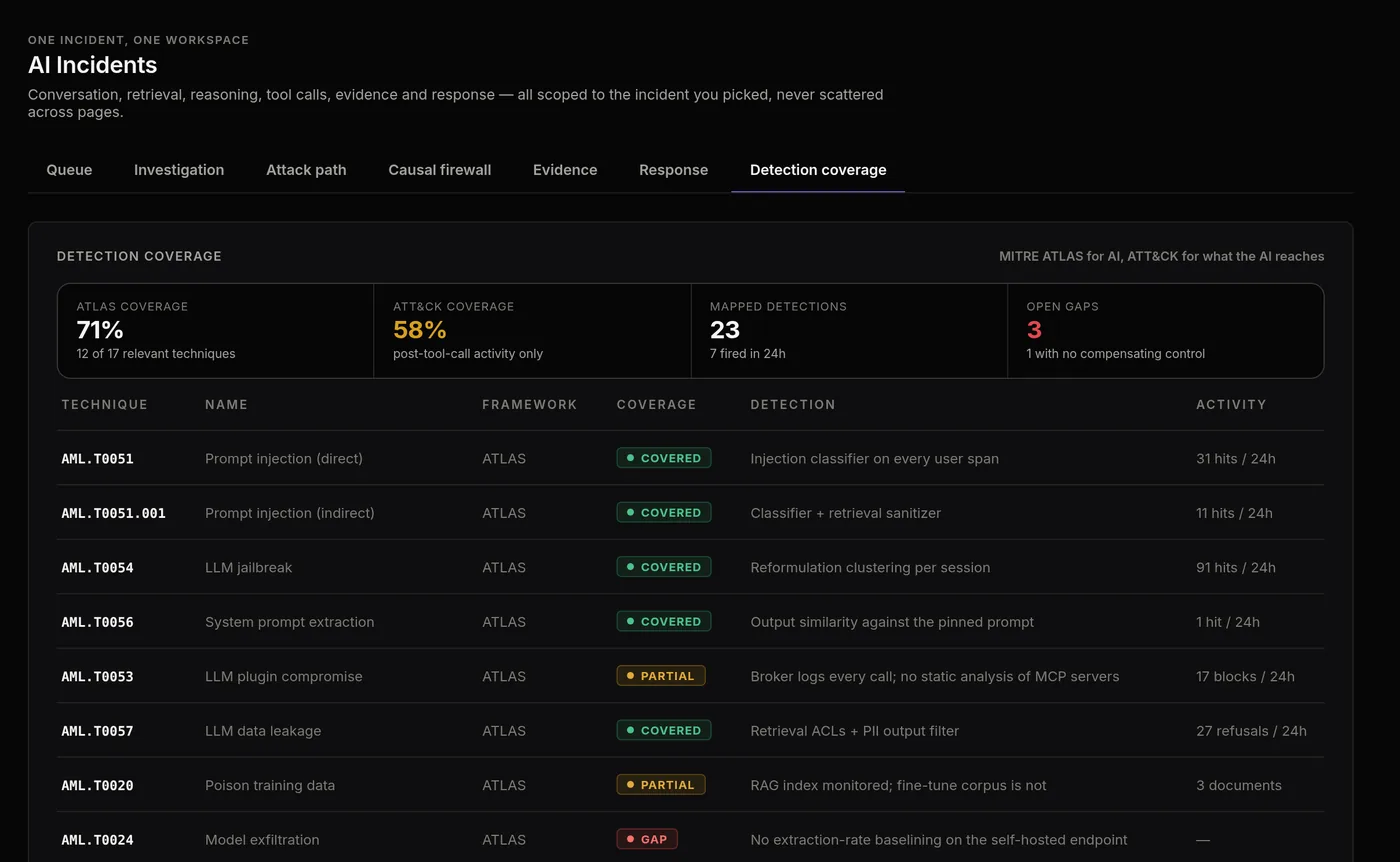
- Correlates findings into incidents with risk scores, attack paths, evidence and response actions.
- Keeps every tenant's rows behind forced row-level security and an append-only audit log.